See, control and prove every use of AI across your organisation.
Your people are already using AI. Zala Proof shows which, by whom and on whose approval. It reads the tools you already own, applies your decisions where AI is used, and puts evidence behind every claim, all on your own site.
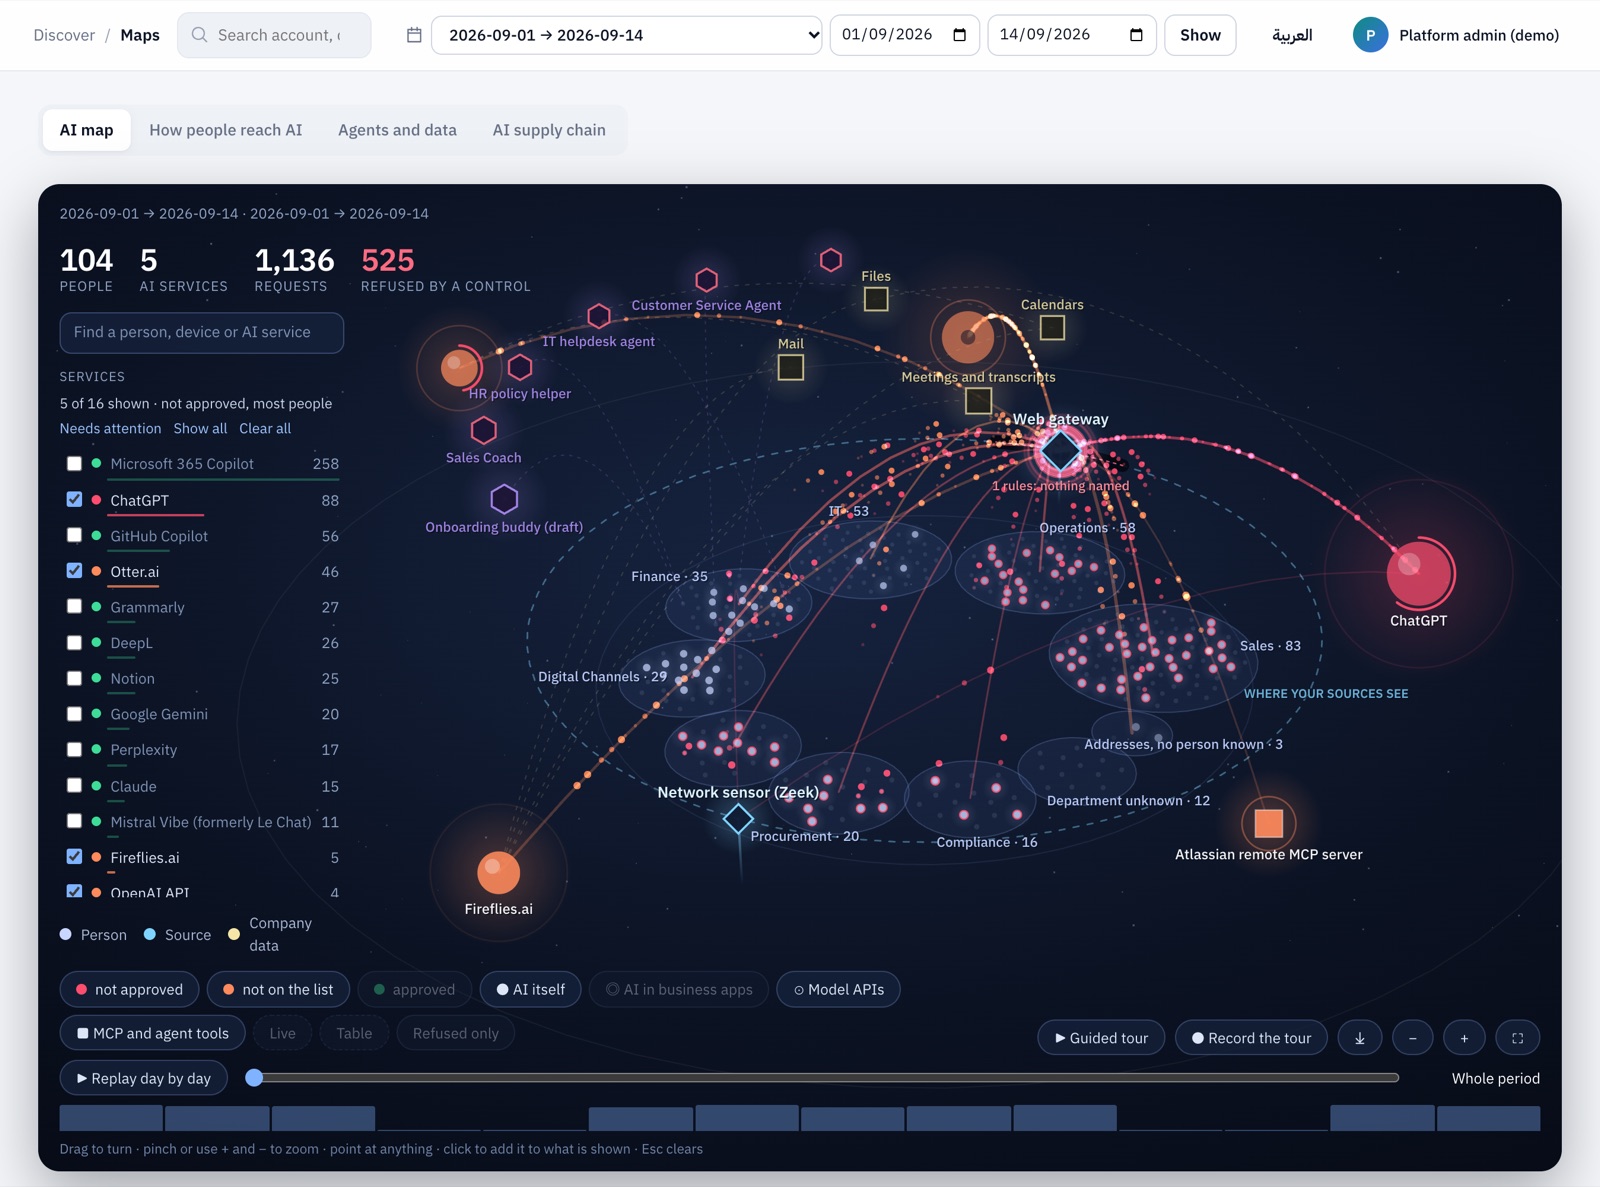
AI arrived before the controls did.
It comes through websites, personal accounts, features switched on inside business apps, desktop tools and agents. No single team sees all of it.
Without AI usage control
AI websites, personal accounts, AI switched on inside business apps, coding agents and their tools.
Sensitive data pasted into a prompt, large uploads, and no record of what kind of data went where.
A policy people can read but no tool enforces. Blocking everything only moves use somewhere you see even less.
Without AI governance
IT, security and the business each hold part of the list, and internal AI systems often sit on none of them.
Nobody is accountable for an AI system, and a high-risk one goes live the same way as a low-risk one.
Decisions live in email. Mapping them to a framework becomes a project every time someone asks.
Without visibility, every later stage fails quietly.
Coverage is not one feature among many. It decides how far you can trust everything after it.
The list misses what nobody reported.
Rules cover only the services you know.
Tests pass on the paths you thought of.
No alert fires for what no source shows.
A clean report gives false comfort.
Zero findings from a channel you do not watch means unknown, not safe.
Good tools, built for other jobs.
Each sees one slice of AI use. Zala Proof does not replace them: it reads them, joins them, and shows what is still missing.
| Tool | Strong at | Where it leaves a gap for AI |
|---|---|---|
| EDR | Managed endpoints | Unmanaged devices, SaaS features, which account was used |
| NDR | Traffic on mirrored links | Off-network users, cloud-to-cloud calls, AI inside SaaS |
| Web gateway, SSE | Web use that passes through it | Traffic that bypasses it; AI under an approved domain |
| DLP | Data on its own channels | No AI inventory; blind on channels it does not cover |
| Identity, SSO | Company sign-ins | Personal accounts; AI apps outside single sign-on |
| SIEM | The logs you send it | Only what is fed in; no AI catalog or policy to compare |
Typical deployments, in our own assessment; it varies by product.
One product across your AI estate.
Start with what you already have, and connect only what you choose.
Coverage and discovery
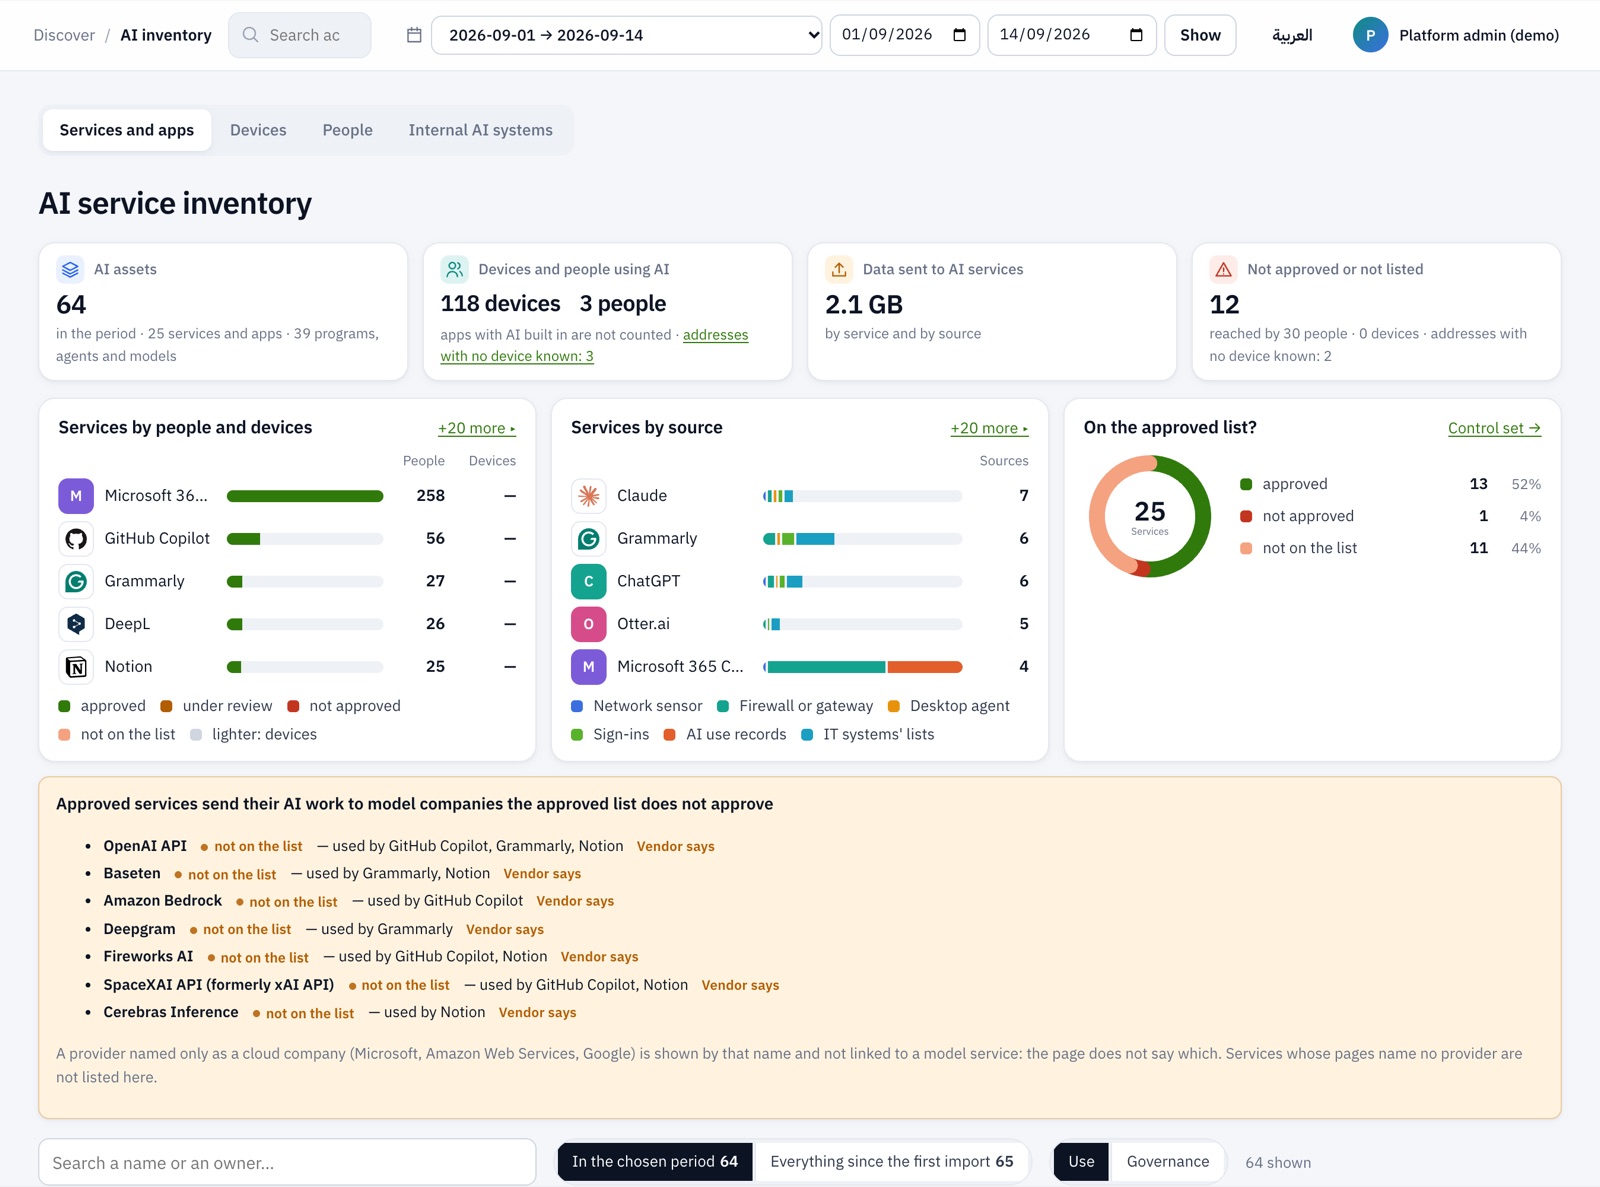
Zala Proof reads the tools you already run, 26 kinds of source in all, and matches what they show against a catalog of over 1,500 AI services. A coverage map says what each source can show and where nothing is connected.
- Websites, desktop programs, agents, MCP servers, model APIs, AI in code
- An inventory of AI services and internal AI, joined across sources
- The model companies behind the services you approved, as the vendor states them
Decide once, apply it where AI is used
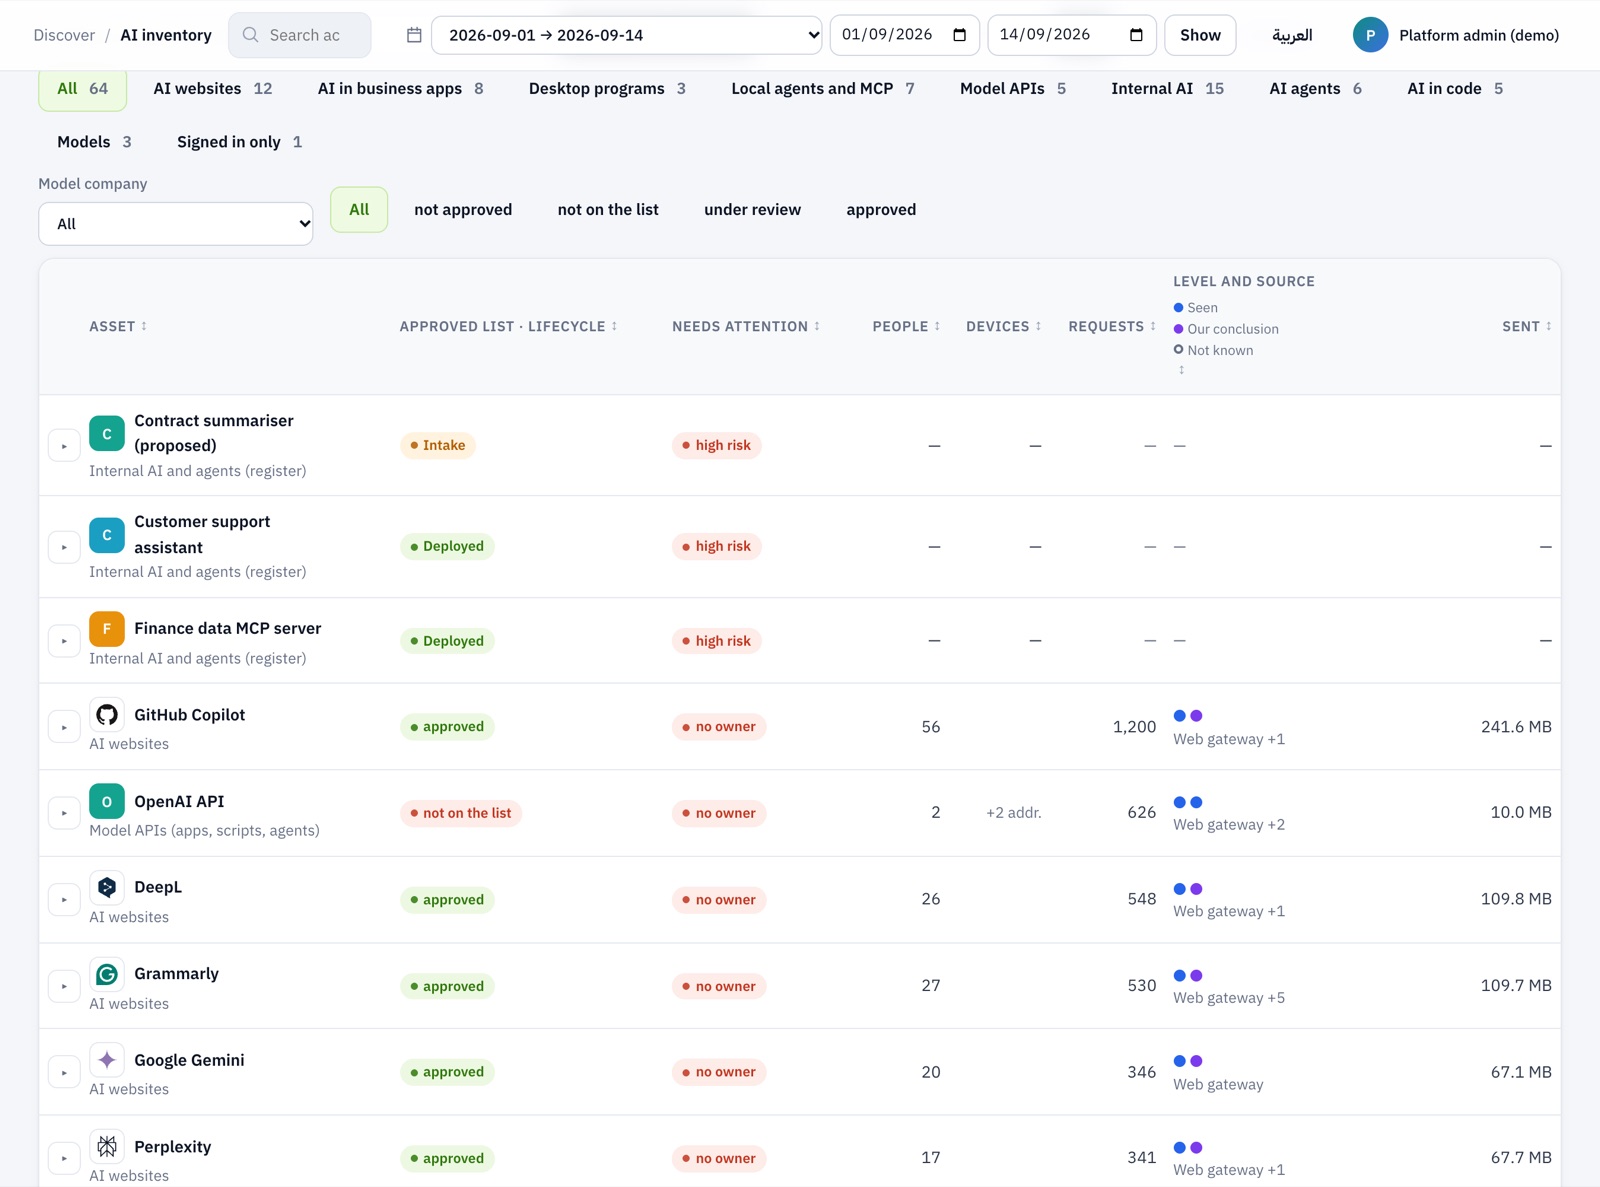
An approved list, attested by your compliance owner. Every AI asset gets an owner, a lifecycle and a risk tier. The browser extension and desktop agent then apply the decision, and response actions run through the security tools you already own.
- Allow, warn or block each AI service in managed Chrome and Edge
- Sensitive data checked before it is sent; the prompt is never reported
- Nothing changes on your systems until a second person approves it
Evidence for every claim, and no blended score
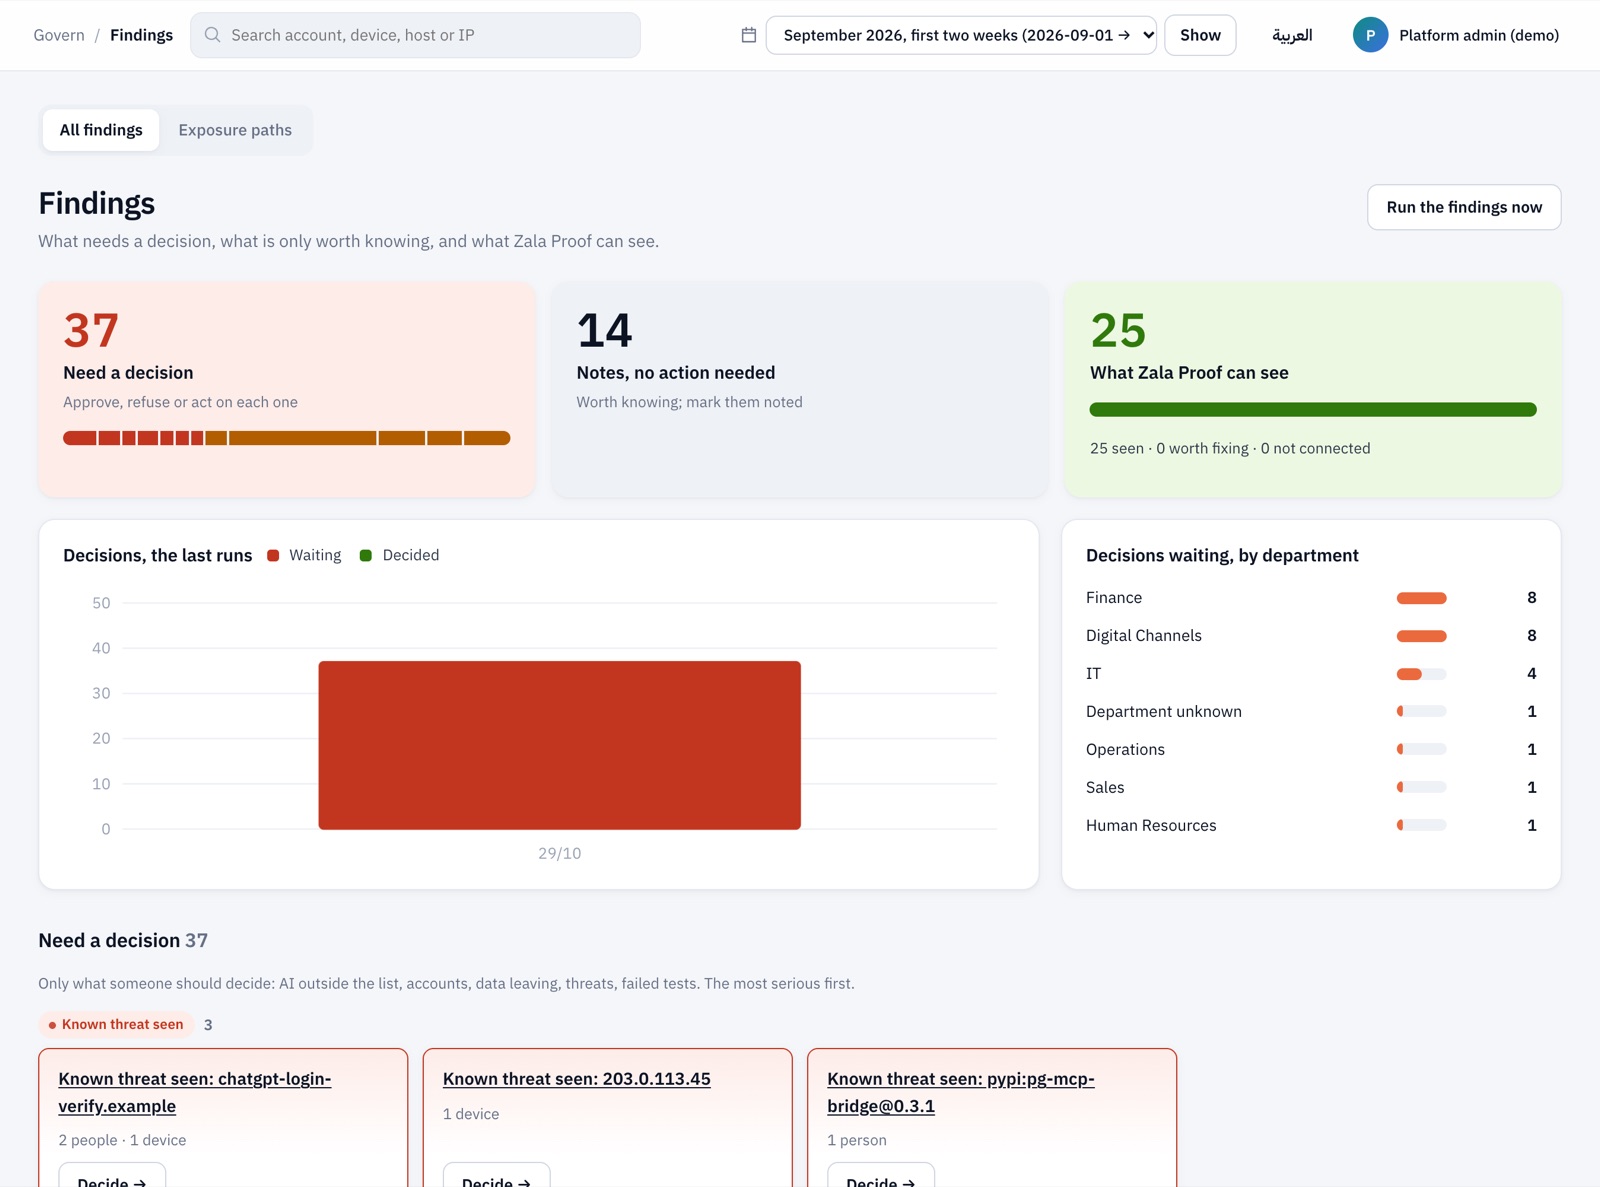
Each claim says what it rests on: seen, you confirmed, vendor says, our conclusion, or not known. Control tests check that a block really blocks. Every decision goes into a hash-chained ledger, and reports go to the board and your auditors.
- Control tests and red-teaming of your own AI apps, in English and Arabic
- An activity timeline for investigations, opened only with a recorded reason
- Decisions mapped to the EU AI Act, ISO/IEC 42001, NIST AI RMF and regional rules
Inside your network, under your control.
A virtual appliance for VMware, Hyper-V, Nutanix or KVM, or containers on your own Linux VM. It needs no general internet access, and Zala has no standing access.
It reads what your tools already record, and the optional network sensor keeps metadata only. Packets are not stored and traffic is not decrypted.
Activity is stored under pseudonyms, with names sealed apart. Your own staff see names, and an administrator can turn that off for anyone. Partners and auditors only ever see pseudonyms.
The whole product and its reports, in both languages, with Arabic-aware checks for sensitive data.
What we are working on now.
Zala Proof is in pilot and moving quickly. This is the work in front of us, stated as it stands.
An assistant on the appliance that answers from your own records and cites them. Counts and lists already answer at once; we are bringing written answers down to seconds on an on-site GPU, in testing today.
Every question that can be answered exactly from the records should not go to a model at all. We keep moving more of them across.
Each source is checked against real samples when it is connected. We are widening the set confirmed on live systems, vendor by vendor.
Turning alerts, investigations and response actions into full cases that hand their lessons back to policy.
Start with what you already have.
A pilot runs on your own data, on your own site. A first picture can come from exported files, with nothing changed on your network. Tell us what you run, and we will show you what it can see.